When Legitimate Commands Become Cyber Threats: Lessons From France's Supermarket Refrigeration Attacks
Hundreds of supermarkets across France recently experienced a major disruption of their refrigeration systems, demonstrating how unauthorized access to operational technology can lead to physical damage, financial losses, and business interruption.
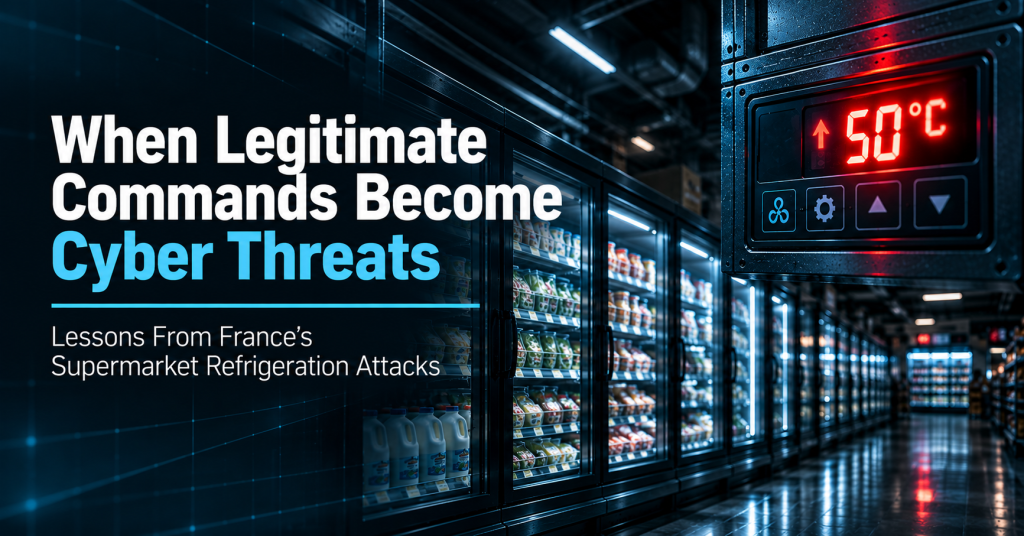
In October 2026, hundreds of supermarkets across France experienced an unusual and costly cybersecurity incident. Attackers reportedly gained remote access to refrigeration management systems and manipulated operating settings, causing equipment designed to preserve perishable products to generate excessive heat. Temperatures reportedly reached as high as 50°C (122°F), with some locations experiencing fires, damaged equipment, and substantial inventory losses.
According to reporting, approximately 700 supermarkets were affected, with retailers facing millions of euros in losses. Rather than simply disabling equipment, attackers reportedly manipulated legitimate operational functions, including extending refrigeration defrost cycles well beyond their normal duration.
The incident illustrates a concerning aspect of operational technology (OT) security: attackers do not always need sophisticated malware to disrupt physical operations. In some cases, unauthorized control over existing functionality can be enough to cause serious damage.
For organizations responsible for critical infrastructure, manufacturing facilities, utilities, and other operational environments, the implications extend well beyond retail. The incident raises important questions about internet-exposed devices, third-party maintenance access, configuration management, and whether existing security monitoring can recognize malicious activity carried out through legitimate system functions.
What Happened to France's Supermarket Refrigeration Systems?
The attacks occurred overnight between October 11 and 12, 2026, when many affected supermarkets were closed and abnormal equipment behavior was less likely to be noticed immediately.
Modern commercial refrigeration systems rely on centralized controllers to regulate temperatures, manage defrost cycles, monitor equipment conditions, and support maintenance operations. These systems frequently include remote management capabilities, allowing technicians and service providers to troubleshoot problems or modify settings without physically visiting each location.
Although these capabilities improve operational efficiency, they can also introduce security risks when management interfaces are exposed to the internet or inadequately protected.
During the French incidents, attackers reportedly accessed refrigeration management systems and modified operational parameters. Reporting from Le Monde indicated that defrost cycles were extended from approximately one hour to eight hours, allowing temperatures to rise significantly while delaying alarms that would normally prompt intervention.
France's national cybersecurity agency, ANSSI, issued an advisory through CERT-FR identifying compromises involving several refrigeration management platforms, including:
- Danfoss AK-SM and AK-SC series: Refrigeration management controllers used to coordinate equipment operation and monitoring.
- Copeland XWEB: Remote monitoring and supervisory systems used in commercial refrigeration environments.
- Dixell XWEB: Refrigeration monitoring and management platforms supporting centralized control and maintenance.
French authorities advised operators to restrict public access to affected management interfaces, review system configurations, secure remote connections, and apply available manufacturer updates.
Although investigations have not conclusively established every intrusion method used across the affected locations, the incident demonstrates how weaknesses in remotely accessible operational equipment can allow attackers to manipulate physical processes.
When Legitimate System Functions Become Security Threats
One of the most important lessons from the incident is that the reported damage resulted from manipulating functions the refrigeration equipment was already designed to perform.
Commercial refrigeration controllers routinely manage defrost cycles to prevent ice accumulation and maintain equipment efficiency. Under normal conditions, the controller temporarily changes operating conditions to remove accumulated ice before returning the equipment to its intended cooling state.
However, when an unauthorized individual gains sufficient access to modify operating parameters, that same functionality can become a mechanism for disruption. An attacker who extends defrost cycles, changes temperature setpoints, or modifies alarm configurations may be able to create unsafe conditions without introducing a separate malicious program into the controller.
This creates an important distinction between a technically valid command and an operationally appropriate command.
Traditional cybersecurity controls frequently focus on detecting malicious software, suspicious network traffic, unauthorized processes, and known attack signatures. Those capabilities remain essential, but operational environments introduce risks that may not be adequately addressed through conventional IT monitoring alone.
For example, a security system might recognize an attempt to execute malicious code on a workstation but fail to identify a refrigeration controller accepting an unusually long defrost cycle through its normal administrative interface.
Understanding whether a command represents a threat requires additional context, including:
- Authorization: Was the command issued by an approved user or maintenance provider?
- Timing: Did the activity occur during an expected maintenance window?
- Operating parameters: Did the requested configuration fall outside established limits?
- Operational impact: Could the change affect equipment safety, availability, or performance?
- Activity patterns: Were similar changes made across multiple systems or facilities?
These considerations demonstrate why OT security must extend beyond determining whether a device is functioning as designed. Organizations also need to understand whether the actions performed by that device are appropriate for the physical process it supports.
The Security Risks of Internet-Exposed Operational Technology
Remote connectivity is now a routine component of industrial and commercial operations. Utilities use connected infrastructure to monitor distributed assets, manufacturers rely on remote maintenance to support production equipment, and commercial facilities use building management systems to control heating, ventilation, refrigeration, and other essential functions.
These connections provide significant operational benefits, but they can also create entry points when equipment is deployed without sufficient access restrictions or maintained beyond its supported lifecycle.
Operational systems often remain in service much longer than conventional IT devices. A controller may have been installed years earlier, configured for remote vendor access, and left largely unchanged because it continues performing its intended function. Over time, the original security assumptions surrounding that equipment may no longer be appropriate.
Several conditions can increase exposure across these environments:
- Publicly accessible management interfaces: Administrative portals or controller interfaces exposed directly to the internet may provide opportunities for unauthorized access.
- Outdated or unsupported equipment: Older devices may contain known vulnerabilities that cannot be remediated through current manufacturer updates.
- Weak authentication and excessive privileges: Shared accounts, insufficient authentication controls, or overly broad permissions can increase the consequences of compromised credentials.
- Persistent third-party connectivity: Vendors and contractors may retain remote access after maintenance activities are completed.
- Incomplete asset inventories: Security teams may lack visibility into devices managed by facilities departments, engineering teams, or external service providers.
- Limited network segmentation: Inadequate separation between management networks and operational equipment can allow unauthorized activity to reach systems responsible for physical processes.
Not every internet-connected operational device is necessarily vulnerable, and remote access is not inherently unsafe. The risk depends on how the connection is secured, what permissions it provides, and whether the organization can identify and respond to misuse.
Why Traditional Detection May Not Recognize Operational Manipulation
Many security monitoring programs were originally designed around enterprise IT environments, where suspicious behavior often involves malware execution, unauthorized access to files, unusual network communications, or attempts to move between systems.
Operational environments present different challenges because the systems being monitored may use specialized protocols, have limited logging capabilities, or lack support for conventional endpoint security tools. More importantly, harmful activity can occur through functions that are entirely legitimate under normal operating conditions.
Consider the difference between an attacker installing malware on an employee's computer and an attacker modifying a temperature setpoint through an authorized management interface. The first scenario may generate recognizable indicators associated with malicious software. The second may appear in system logs as a routine configuration change, even when the consequences are significant.
Effective OT monitoring should consider both cybersecurity activity and the behavior of the physical systems being protected. Depending on the environment and available telemetry, useful indicators may include:
- Unexpected configuration changes outside approved maintenance windows.
- Administrative access from unfamiliar sources or at unusual times.
- Changes to critical setpoints, operating schedules, or alarm thresholds.
- Repeated modifications across multiple controllers or facilities.
- Operational behavior that deviates significantly from established baselines.
For refrigeration infrastructure, monitoring may focus on unusual defrost schedules, unexpected temperature increases, or changes to alarm configurations. In a water utility, the relevant activity might involve modifications to chemical dosing parameters, while manufacturing environments may prioritize unauthorized changes to production equipment.
The underlying objective is the same: identify behavior that could threaten the operation, even when the individual commands appear technically legitimate.
Achieving this requires coordination between cybersecurity teams and personnel who understand the processes being controlled. Combining those perspectives can improve detection accuracy and help organizations prioritize events according to their potential consequences.
The Challenges of Securing Distributed and Legacy OT Environments
The scale of the French attacks highlights the difficulties organizations face when managing operational technology across numerous locations.
A supermarket chain operating hundreds of stores may rely on a combination of refrigeration controllers, building automation systems, network equipment, and vendor-managed services. Equipment models, firmware versions, maintenance arrangements, and security configurations may differ substantially between locations.
These inconsistencies can make it difficult to establish uniform security controls, particularly when operational equipment is managed separately from the organization's central IT infrastructure.
Legacy equipment introduces additional challenges. Industrial controllers and building management systems are often designed to remain operational for many years, and replacing them may require compatibility testing, specialized installation, and operational downtime.
While older equipment may remain mechanically reliable, its cybersecurity protections can become increasingly outdated. Security researchers had previously documented vulnerabilities affecting certain refrigeration management platforms, and some affected products were reportedly running outdated firmware.
Organizations managing distributed or legacy environments should prioritize:
- Asset visibility: Identifying operational devices, their locations, firmware versions, and network connections.
- Configuration consistency: Determining whether similar systems have different security settings or outdated software.
- Vendor coordination: Understanding which third parties maintain access to equipment across facilities.
- Centralized monitoring: Collecting meaningful security and operational information from geographically dispersed locations.
- Lifecycle management: Identifying unsupported equipment and planning appropriate updates, isolation, or replacement.
A weakness affecting one controller may appear localized, but if the same configuration or vulnerability exists across hundreds of locations, the potential consequences become substantially greater.
Understanding the Physical and Financial Consequences
The French supermarket attacks demonstrate why OT cybersecurity risk should be evaluated according to potential operational consequences rather than technical severity alone.
Traditional IT incidents often involve data theft, credential compromise, ransomware, or disruptions to business applications. OT incidents can introduce additional risks because the affected systems control equipment and processes operating in the physical world.
In the refrigeration attacks, reported consequences included destroyed inventory, damaged equipment, interrupted store operations, and substantial financial losses. Recovery required more than restoring access to computer systems; affected retailers also needed to assess equipment conditions, remove spoiled products, restore safe operating temperatures, and replenish inventory.
Similar incidents in other industries could affect production availability, equipment integrity, environmental conditions, or essential services. A compromised building management system could disrupt conditions in a healthcare facility, while unauthorized modifications to manufacturing equipment could damage products or interrupt production.
These scenarios illustrate why organizations should evaluate the relationship between cybersecurity vulnerabilities and the processes those vulnerabilities could affect.
A relatively small controller may represent a significant risk if it supports an essential operational function. Understanding those distinctions helps organizations prioritize security investments according to the exposures with the greatest potential consequences.
Practical Steps to Strengthen Operational Security
The French refrigeration incident provides an opportunity for organizations to evaluate whether their current security controls adequately address remotely managed operational equipment.
Several practices can help reduce exposure and improve readiness:
1. Establish visibility into operational assets and external exposure. Maintain accurate inventories of operational equipment, including management interfaces, remote access services, firmware versions, and network connections. Identify devices accessible from the public internet and determine whether that connectivity is necessary.
2. Strengthen remote access and vendor management. Apply appropriate authentication, authorization, and monitoring controls to remote maintenance connections. Regularly review third-party permissions, restrict administrative privileges, and remove access that is no longer required.
3. Monitor critical configuration changes. Identify operating parameters that could affect equipment safety or availability, establish approved ranges, and monitor unexpected modifications, particularly those occurring outside normal maintenance periods.
4. Address unsupported equipment and known vulnerabilities. Coordinate firmware updates and remediation with engineering teams and vendors. Where updates are unavailable, evaluate compensating controls such as network isolation, restricted access, and enhanced monitoring.
5. Improve coordination between security and operations. Establish clear responsibilities and communication between cybersecurity teams, engineers, facilities personnel, and external service providers. Joint incident response exercises can help teams recognize and respond to operational threats.
6. Prepare for safe recovery. Maintain appropriate configuration backups, document restoration procedures, and establish criteria for returning affected equipment to service. Recovery plans should address both the physical consequences of an incident and the security weaknesses that allowed it to occur.
One particularly important recommendation from CERT-FR concerns the limitations of resetting compromised controllers. Restoring a device to factory settings may remove unauthorized configuration changes, but it does not necessarily correct the vulnerability or exposure that allowed the compromise.
If the same controller remains publicly accessible with outdated firmware or inadequate authentication controls, it may be vulnerable to another attack. Effective recovery must therefore address the underlying security conditions, not simply restore normal equipment operation.
Five Questions Organizations Should Be Asking
The French attacks provide a useful starting point for discussions between cybersecurity leaders, operational personnel, facilities managers, and executive teams.
Organizations should consider whether they can confidently answer the following questions:
- Which operational devices and management interfaces are accessible from outside our network?Understanding external exposure is essential for identifying unnecessary access paths and prioritizing remediation.
- Who can modify critical operating parameters? This includes employees, contractors, service providers, shared accounts, and remote maintenance arrangements.
- Would our monitoring identify a dangerous configuration change made through a legitimate function?Detection capabilities should consider operational context, not simply whether a command originated from recognized software or an authorized interface.
- Which systems could create physical, financial, or safety consequences if manipulated? Risk assessments should connect technical exposures to the operational processes and business functions they support.
- Could we respond effectively if similar systems were compromised across multiple facilities? Incident response planning should account for distributed environments, vendor coordination, operational safety, and recovery.
These questions help move the discussion beyond individual vulnerabilities toward a more complete understanding of operational cybersecurity risk.
Strengthening Security Where Cyber Risks Meet Physical Operations
The refrigeration attacks in France demonstrate how cybersecurity weaknesses can have consequences far beyond the systems initially compromised. Equipment that has operated reliably for years may still present significant exposure if remote access, configuration management, and security monitoring have not kept pace with evolving threats.
The incident reinforces the importance of understanding operational technology in context. Identifying an exposed controller is an important first step, but organizations also need to know what that controller manages, who can access it, which functions could be misused, and what consequences could result from unauthorized changes.
At Critical Path Security, we help organizations identify security exposures, assess operational risk, and strengthen detection and response capabilities across environments where cybersecurity incidents can affect real-world operations.
Our approach emphasizes understanding the relationship between technical vulnerabilities and operational consequences, allowing organizations to make more informed decisions about where security improvements are needed most.
The central lesson from France's supermarket refrigeration attacks is that legitimate system functionality can become a source of significant disruption when access and oversight are insufficient. Protecting operational environments requires visibility into connected assets, effective controls over critical functions, and the ability to recognize when normal capabilities are being used in abnormal or dangerous ways.